The Voice Sounds Real. The Identity May Not Be: Defending Healthcare Against AI Voice Phishing
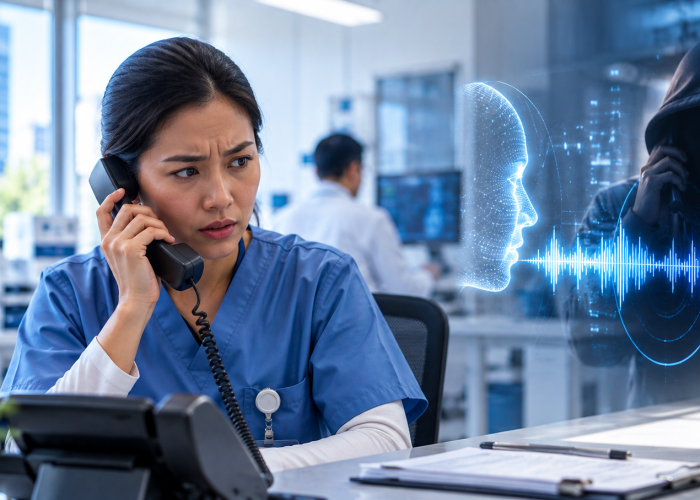
The phone rings at a hospital IT help desk, and the caller sounds exactly like a senior executive. The voice is familiar, the request is urgent, and the caller says an MFA problem is preventing access to an important system. With AI voice phishing in healthcare, recognizing someone’s voice can no longer provide reliable evidence that the person on the other end is who they claim to be.
Generative AI has made realistic impersonation easier to create and use in social-engineering campaigns. In May 2025, the FBI warned that malicious actors were sending AI-generated voice messages and text messages while impersonating senior U.S. officials, and the Bureau reiterated the threat in a December 2025 update. The FBI advises independently verifying suspicious callers or messages through trusted contact information rather than assuming a familiar voice is authentic. (FBI)
For hospitals, physician practices, outpatient facilities, health systems, and other U.S. healthcare organizations, this changes an important security assumption. A person’s voice, title, caller ID, or knowledge of internal terminology should not independently authorize a sensitive action. Healthcare organizations need to move from recognition-based trust to verification-based trust.
Social Engineering Has Moved Beyond Email
Healthcare cybersecurity awareness programs have traditionally placed considerable emphasis on phishing emails. Email remains important, but modern social engineering can also arrive through telephone calls, SMS messages, video, collaboration platforms, and AI-generated audio. HHS warns that social-engineering attacks can involve emails, texts, calls, and even videos that appear to originate from trusted individuals, companies, or institutions. (HHS.gov)
The attacker’s objective is often to persuade a legitimate employee to perform an action on the attacker’s behalf. Instead of technically defeating a firewall or exploiting a server, the attacker attempts to exploit the organization’s business processes. HHS notes that social engineering can succeed precisely because manipulating a person may sometimes be easier than directly breaching technical defenses. (HHS.gov)
That creates risk across multiple healthcare departments. IT help desks, practice administrators, finance teams, payroll employees, clinical personnel, billing departments, and cloud administrators can all perform actions valuable to an attacker. The target is therefore not limited to the cybersecurity team.
How an AI Voice Impersonation Attack Could Work
Consider a hypothetical hospital where a help-desk employee receives a call appearing to come from the CIO. The caller knows the executive’s name, job title, employer, and enough organizational information to sound credible. An AI-generated voice makes the caller sound remarkably similar to the real executive.
The caller claims to be locked out before an urgent meeting and requests a password reset. Moments later, the request expands to resetting MFA or enrolling a new authentication method. The employee believes they are helping an executive solve a legitimate business problem.
This is where the security failure can occur. The employee may follow an approved technical process but initiate it for the wrong person. The vulnerability is not necessarily the password-reset technology—it is the identity-verification process surrounding it.
AI Voice Impersonation Is Already a Real Threat
The FBI’s May 2025 warning documented malicious actors impersonating senior U.S. officials using text messages and AI-generated voice messages. The campaign was not a healthcare-specific incident, so it should not be represented as evidence that hospitals were targeted in that particular operation. It does, however, demonstrate that AI-generated voice impersonation is being used in real-world malicious campaigns. (FBI)
The FBI describes vishing as malicious targeting through voice messages and notes that AI-generated voices can be used to impersonate known contacts. Attackers may combine public information, altered contact details, stolen account information, and synthetic audio to increase credibility. The agency warns that AI-generated content has advanced enough that determining authenticity can be difficult. (FBI)
The underlying pattern is familiar: impersonate somebody trusted, create urgency, and persuade the target to act. Generative AI does not invent social engineering, but it can make impersonation more convincing. Healthcare security processes need to assume that convincing audio can be fabricated.
Why Healthcare Help Desks Are Identity-Security Boundaries
Organizations often place strong controls around privileged administrators while viewing help desks primarily as support functions. Yet help-desk personnel may have another powerful capability: restoring access when normal authentication fails. That effectively makes the help desk part of the organization’s identity-security perimeter.
Depending on the environment, support personnel may be able to reset passwords, unlock accounts, reset MFA, change recovery information, register devices, or issue temporary credentials. Each capability exists for legitimate operational reasons. Each can also become valuable to an attacker trying to bypass normal authentication.
Strong MFA provides less protection if an attacker can manipulate the recovery workflow used when MFA fails. Account recovery should therefore receive security controls proportional to the access it can restore. The more privileged the identity, the stronger that recovery process should be.
A Password Reset Is a Security Event
Healthcare organizations should stop treating high-risk password and MFA resets as purely routine support transactions. A successful reset can change who controls an account. For administrators and other sensitive identities, that makes recovery activity security-relevant.
A request to disable MFA deserves even greater scrutiny. Attackers may frame the request as a technical problem, lost device, travel issue, or urgent business requirement. Urgency should increase verification rather than reduce it.
Organizations should define which recovery activities require escalation. Resets involving executives, privileged administrators, finance personnel, remote-access accounts, and sensitive clinical systems may justify additional verification or approval. Help-desk staff should have clear procedures rather than needing to improvise under pressure.
Never Authenticate Sensitive Requests by Voice Alone
A recognizable voice should not independently authorize a sensitive transaction. The same principle should apply to caller ID, a familiar writing style, a person’s job title, or knowledge of internal information. All of these signals can potentially be spoofed, stolen, researched, or generated.
This is particularly important for password resets, MFA changes, privileged-access requests, payment instructions, recovery-method changes, and sensitive information requests. Organizations should establish an independent verification process for high-impact actions. The verification channel should not depend solely on information supplied during the suspicious interaction.
The objective is not to teach employees how to perfectly recognize synthetic audio. It is to design a workflow where correctly identifying a deepfake is unnecessary. Even a flawless imitation should fail if the caller cannot satisfy independent verification requirements.
Call Back Through a Trusted Channel
One practical control is an independently initiated callback. Instead of calling the number supplied by the caller or trusting displayed caller ID, staff can use contact information already stored in an approved organizational directory. This creates a separate verification channel.
The FBI recommends independently identifying contact information and contacting the purported person to verify authenticity when suspicious communications occur. (FBI) The important word is independently because using contact details provided by the suspected attacker defeats much of the purpose.
Healthcare organizations can build this into standard procedures. Employees should know exactly where trusted contact information is maintained and when callbacks are mandatory. A verification process is most effective when employees do not need to invent it during a stressful call.
Strengthen MFA Recovery Procedures
MFA protects accounts by requiring more than a password, but the recovery process can become a secondary path around that protection. If an attacker can persuade support staff to replace an authentication method, the strength of the original MFA implementation may become irrelevant. Recovery therefore needs to be designed as part of authentication security.
High-risk recovery can require combinations of manager approval, known-device verification, existing trusted communication channels, security-team review, or other independent identity checks. The appropriate process depends on the organization’s technology and operational needs. Higher-privilege accounts should generally receive greater scrutiny.
Organizations should also log and monitor MFA changes. A password reset immediately followed by enrollment of a new authentication method may deserve additional review, particularly for privileged identities. Identity telemetry can help detect when social engineering has successfully crossed into account takeover.
Use Phishing-Resistant MFA Where Possible
CISA recommends organizations work toward phishing-resistant MFA and identifies FIDO/WebAuthn as the widely available phishing-resistant authentication option. Unlike authentication methods that can be entered into an attacker-controlled website, FIDO authentication is designed to resist credential phishing. (CISA)
Healthcare organizations can prioritize stronger MFA for privileged administrators, executives, IT support personnel, finance staff, email, remote access, and other sensitive systems. CISA also recommends prioritizing MFA for administrative access and employees handling sensitive information. (CISA)
Phishing-resistant MFA does not make voice impersonation disappear. An attacker may instead attempt to convince support personnel to reset or replace that authentication mechanism. Strong authentication and strong recovery processes therefore need to operate together.
Require Additional Approval for Unusual Requests
Certain requests should automatically trigger additional scrutiny regardless of who appears to be making them. “Disable my MFA,” “give me administrator access,” or “change these payment instructions immediately” should never become routine merely because the caller sounds senior or frustrated. Organizational hierarchy should not override verification procedures.
Dual approval can be useful for particularly sensitive actions. One employee can initiate the process while another verifies or authorizes the change. This reduces the likelihood that a single successful social-engineering interaction results in immediate compromise.
The process should also protect employees from pressure. Help-desk and finance personnel need explicit organizational authority to delay suspicious requests while verification occurs. Security procedures work better when employees know leadership expects them to follow the process even when the apparent requester is an executive.
Finance and Billing Teams Need Voice-Deepfake Training Too
IT is not the only department exposed to AI impersonation. Finance personnel may receive urgent requests to change payment details, billing staff may receive requests involving account information, and payroll teams may be asked to modify direct-deposit instructions. AI-generated voices can add credibility to familiar fraud scenarios.
Healthcare organizations should therefore avoid limiting deepfake awareness training to technical employees. Practice managers, administrative personnel, finance, human resources, billing teams, clinical leadership, and executive assistants can all encounter impersonation attempts. Training should reflect the transactions each role can authorize.
A useful exercise can present an apparently urgent executive request and ask employees what verification procedure should occur next. The goal is not to identify subtle imperfections in the fake. It is to reinforce the correct business process.
PHI Requests Require Identity Verification
AI impersonation can also create privacy risks. An attacker could impersonate a patient, physician, vendor, public official, or another trusted person while requesting sensitive information. A convincing voice should not replace established verification procedures for protected health information.
Under the HIPAA Privacy Rule, covered entities generally must verify the identity and authority of a person requesting PHI when that identity or authority is not already known, subject to the applicable provisions and exceptions. HHS guidance also explains that the Privacy Rule does not prescribe one universal technical verification method, allowing organizations to use reasonable processes appropriate to the circumstances. (HHS.gov)
This distinction is valuable in the deepfake era. The question should not be whether somebody sounds like the physician, executive, or patient expected on the call. The question is whether the organization’s established process has appropriately verified the person and their authority.
Deepfake Detection Alone Is Not Enough
Technology may increasingly help organizations identify synthetic audio and manipulated video. Detection can provide another useful security signal, but it should not become the primary authorization mechanism. Generative technologies and detection methods will continue evolving against each other.
A more durable defense is to build sensitive workflows that do not depend on voice authenticity. An attacker may successfully clone the CEO’s voice, but the attacker should still be unable to reset the CEO’s MFA without satisfying separate verification requirements. A synthetic voice can defeat recognition without necessarily defeating a well-designed transaction.
This is the principle of verification-based trust. Instead of asking employees to determine whether every interaction is real, organizations define objective requirements before high-impact actions can occur. The fake can sound perfect while the transaction still fails.
Healthcare Security Awareness Needs to Evolve
Healthcare cybersecurity training should reflect the communication channels employees actually use. HHS’s Health Industry Cybersecurity Practices resources identify social engineering as one of the major threats facing the healthcare and public health sector, and HHS provides dedicated healthcare social-engineering training resources. (HHS Cyber Gateway)
Training scenarios can include executive voice impersonation, fake help-desk calls, MFA-reset requests, vendor impersonation, PHI requests, and urgent payment changes. Employees should learn both the warning signs and the exact verification process expected by their organization. Awareness without a defined response procedure leaves employees knowing something feels suspicious but unsure what to do.
Exercises should also include senior leadership. Executives need to understand that employees may deliberately delay unusual requests made in their name. A culture that rewards verification makes social engineering more difficult.
How Tempest Healthcare IT Helps Healthcare Organizations
At Tempest Healthcare IT, we help U.S. healthcare organizations evaluate cybersecurity risks involving identities, access controls, endpoints, cloud platforms, and human-driven attack paths. Healthcare-focused security assessments, penetration testing, HIPAA security reviews, phishing awareness, Microsoft security solutions, and incident-response planning can help identify workflows where social engineering could bypass otherwise strong technical controls.
For hospitals, physician practices, specialty clinics, diagnostic facilities, and other healthcare providers, identity security should extend beyond login screens. Password recovery, MFA resets, privileged-access changes, vendor support, and PHI verification can all become part of the attack surface. Evaluating those processes helps organizations understand what happens when an attacker chooses persuasion instead of malware.
Final Thoughts
AI voice phishing in healthcare reinforces a fundamental cybersecurity lesson: familiarity is not authentication. The FBI’s documented warnings about AI-generated voice impersonation demonstrate that synthetic audio is already being incorporated into malicious campaigns, while HHS guidance emphasizes the continuing importance of social-engineering awareness and appropriate identity verification. (FBI)
Healthcare organizations should strengthen account recovery, use phishing-resistant MFA where practical, independently verify unusual requests, train employees for voice-based impersonation, and require additional approval for high-impact actions. The voice can be cloned; the verification process should not be. For more practical guidance on healthcare cybersecurity, identity security, HIPAA compliance, phishing defense, and cyber resilience, follow Tempest Healthcare IT on LinkedIn: Tempest Healthcare IT on LinkedIn