You Did Not Lose Your Password. You Gave an App Permission: Understanding OAuth Security in Healthcare
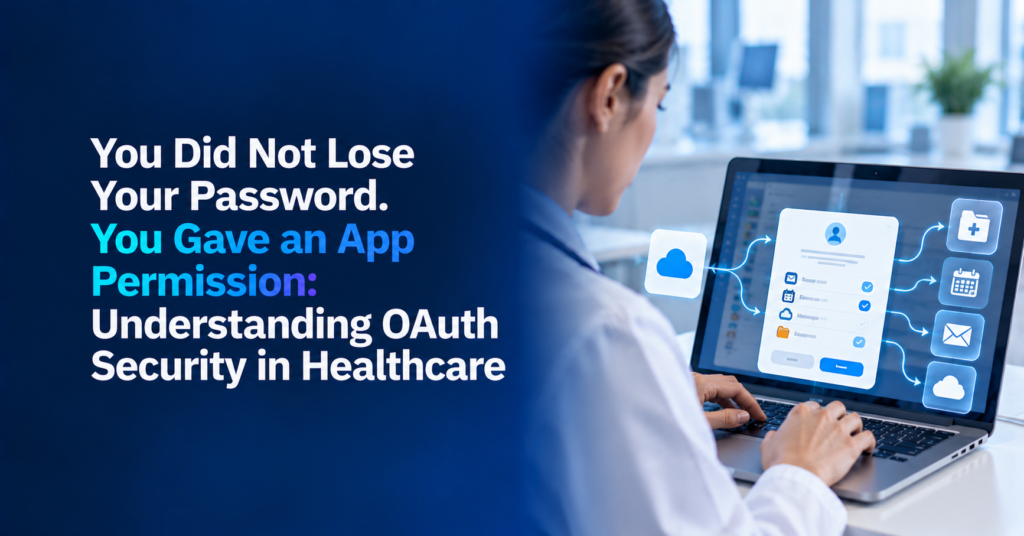
A healthcare employee discovers a productivity application that could help summarize meetings, organize documents, automate administrative tasks, or manage research. Instead of creating another password, the employee selects “Sign in with Microsoft,” sees a familiar consent screen, and clicks Accept.
Below the Operating System: Why Medical Device Firmware Security Matters in Healthcare
Medical device firmware security addresses a layer of healthcare technology that often receives less attention than operating systems, applications, and network controls. A healthcare security team may isolate a suspicious device, reinstall software, reset its configuration, and scan the system until everything appears clean.
When One Hospital Goes Offline: Why Healthcare Ransomware Resilience Is a Regional Patient-Safety Issue
Healthcare ransomware resilience is no longer only about whether one hospital can restore its servers after a cyberattack. A ransomware incident at one healthcare organization can change ambulance routes, increase emergency department demand, delay treatment, and place additional pressure on hospitals that were never technically compromised.
The Voice Sounds Real. The Identity May Not Be: Defending Healthcare Against AI Voice Phishing
With AI voice phishing in healthcare, recognizing someone’s voice can no longer provide reliable evidence that the person on the other end is who they claim to be. Generative AI has made realistic impersonation easier to create and use in social-engineering campaigns.
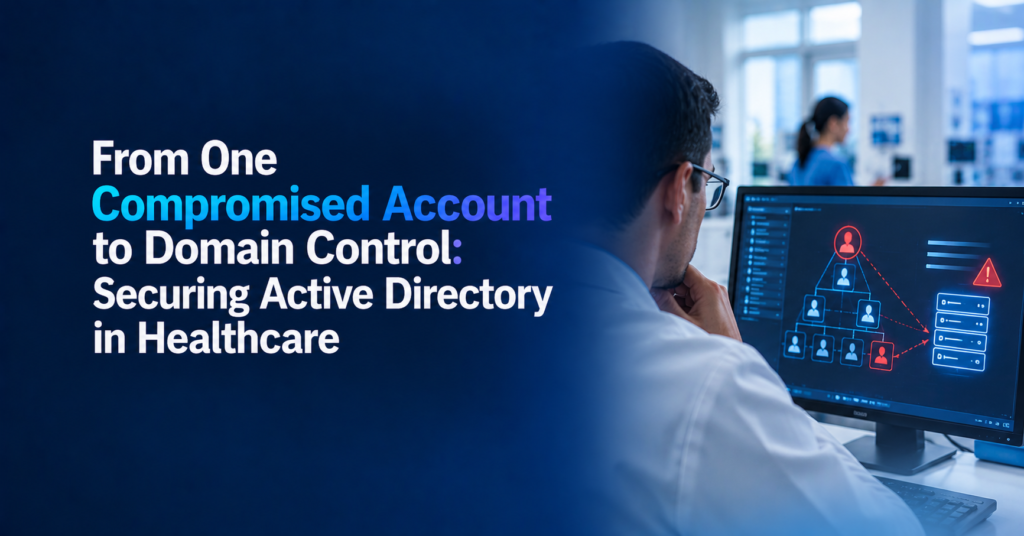
From One Compromised Account to Domain Control: Securing Active Directory in Healthcare
Active Directory security in healthcare can determine whether a phishing incident remains limited to one employee workstation or develops into an organization-wide cyberattack. An attacker who compromises an ordinary healthcare employee may initially have very little access, but the first device is often only the beginning.
Beyond Encryption: How Confidential Computing Protects Healthcare Data While It Is Being Used
Confidential computing in healthcare addresses a security problem that traditional encryption does not fully solve: protecting sensitive patient information while software is actively using it. Healthcare organizations have spent years strengthening encryption for databases, backups, cloud storage, and network connections, but eventually applications need to decrypt information so it can be processed.