Below the Operating System: Why Medical Device Firmware Security Matters in Healthcare
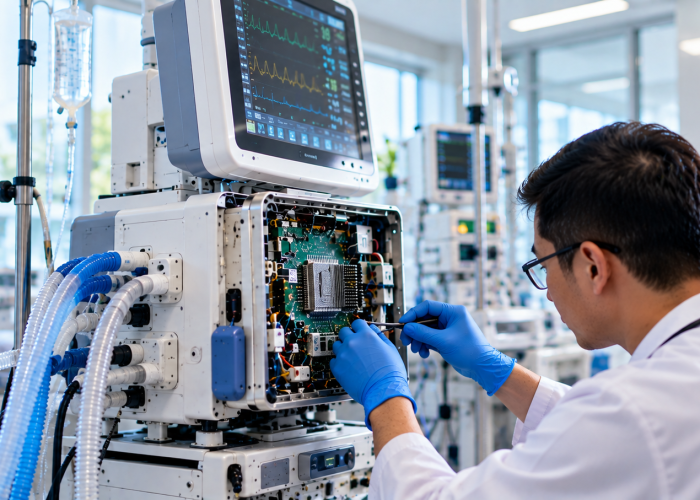
Medical device firmware security addresses a layer of healthcare technology that often receives less attention than operating systems, applications, and network controls. A healthcare security team may isolate a suspicious device, reinstall software, reset its configuration, and scan the system until everything appears clean. Yet firmware can sit underneath all of those layers and continue influencing how the device boots, communicates, and interacts with hardware. Pasted markdown
For hospitals, physician practices, diagnostic centers, and other healthcare organizations, that distinction matters because connected medical devices may remain in service for years. A device can continue performing its clinical function reliably even while some of its underlying technology becomes harder to support. If the low-level code controlling that device becomes vulnerable or compromised, traditional operating-system security may not provide the whole picture.
This does not mean firmware malware is widespread across healthcare environments. It means firmware is a technically credible attack surface that deserves consideration in medical device cybersecurity architecture. Healthcare organizations should understand how devices protect, verify, update, and recover the code running below the operating system.
Where Firmware Fits in the Technology Stack
A simplified way to think about a connected device is: Applications → Operating System → Firmware → Hardware. Most endpoint security tools operate primarily within or alongside the operating system, where they can inspect processes, files, network activity, and user behavior. Firmware operates at a lower level and may execute before the operating system even starts.
MITRE ATT&CK documents adversary techniques involving firmware under its Pre-OS Boot category. These techniques can provide persistence below conventional host-based security controls, which may make malicious modifications difficult to detect using tools that rely on the operating system itself. Pasted markdown
NIST’s Platform Firmware Resiliency guidance makes a similar point. Sophisticated attackers may attempt to modify firmware to maintain persistence, disrupt operations, weaken system security, or support additional malicious activity. For healthcare organizations, the lesson is that trust needs to extend beneath the operating system.
Why a Normal Reimage May Not Always Be Enough
If an ordinary application is compromised, removing or reinstalling the application may resolve the problem. If the operating system itself is compromised, wiping the device and rebuilding the operating system may restore the system to a trustworthy state. Firmware compromise creates a different remediation challenge.
Because firmware can reside in nonvolatile memory outside the normal operating-system filesystem, some malicious changes may survive a conventional reinstallation. NIST notes that corrupted platform firmware can be difficult to repair and may sometimes require reprogramming or vendor-supported recovery. Pasted markdown
This changes an important incident-response question. Instead of asking only, “Is the operating system clean?”, security teams may sometimes need to ask, “Can we trust this device from the firmware layer upward?” That question becomes more relevant when suspicious behavior persists after traditional remediation.
Why Firmware Security Matters for Medical Devices
Connected medical technology can include much more than an application and an operating system. Devices may contain bootloaders, wireless components, network interfaces, embedded operating systems, storage controllers, third-party libraries, firmware modules, and vendor management software. Each component may have its own lifecycle.
The clinical function of a device may remain perfectly usable while supporting components become older or less well supported. FDA recognizes medical device cybersecurity as a total product lifecycle issue, meaning cybersecurity does not end once the device enters service. Pasted markdown
This is particularly important for long-lived devices. A device deployed today may still be in use years after its original software stack was designed. Healthcare organizations should therefore consider firmware support, update mechanisms, and recovery capabilities as part of the device’s ongoing cybersecurity posture.
Firmware Updates Are Both Necessary and Powerful
Firmware updates are essential because they can correct vulnerabilities and improve device security. At the same time, an update mechanism is inherently powerful because it changes low-level code controlling the hardware. That means the device must be able to distinguish an authorized update from a malicious one.
FDA’s 2026 medical-device cybersecurity guidance recommends verifying the authenticity and integrity of firmware and software. It specifically emphasizes cryptographic authentication, rejecting updates that fail verification, using signed updates, and validating software, firmware, and configurations before execution. Pasted markdown
NIST’s IoT cybersecurity baseline similarly identifies secure updating as an important device capability. The underlying principle is straightforward: a connected medical device should not blindly trust an update file simply because someone has presented it to the device.
Why Signed Firmware Updates Matter
Cryptographically signed firmware helps a device verify that an update came from an approved source and was not modified after signing. This reduces the chance that unauthorized or manipulated firmware is accepted during the update process. It also creates a stronger trust relationship between the manufacturer and the device.
Signed updates can also help defend against rollback or downgrade attacks. An attacker may attempt to install an older firmware version containing known vulnerabilities even if the current version is secure. Devices should therefore verify both authenticity and whether the requested version is permitted.
Healthcare organizations should ask vendors how firmware signing works, how signing keys are protected, and what happens if those keys are compromised. A signed update is only as trustworthy as the infrastructure used to create and authorize it.
Secure Boot Can Establish Trust During Startup
Secure boot is another important control in medical device firmware security. Instead of automatically executing every low-level component during startup, a secure boot process can verify that firmware and boot software are authorized and unchanged. This helps establish a root of trust before the operating system begins running.
NIST’s firmware resiliency model organizes the problem around three fundamental capabilities: Protect, Detect, and Recover. Firmware should be protected from unauthorized modification, unauthorized changes should be detectable, and the system should have a path back to a trustworthy state after corruption. Pasted markdown
This model is especially useful during procurement. The question is not merely whether the device accepts firmware updates, but whether it verifies those updates, protects the startup chain, and supports recovery if low-level code becomes damaged or compromised.
Firmware Security Begins With Asset Inventory
Healthcare organizations cannot respond quickly to a firmware vulnerability if they do not know which devices contain the affected firmware. HHS’s Healthcare and Public Health Cybersecurity Performance Goals identify Asset Inventory as an important security practice, including the need to identify known, unknown, unmanaged, and shadow assets. Pasted markdown
For connected medical devices, an effective inventory can include:
- Manufacturer and model
- Serial number
- Firmware version
- Software version
- Network location
- Clinical owner
- Support status
- Available updates
- Known vulnerabilities
- Vendor security contact
When a new vulnerability is announced, the organization should be able to answer, “Which affected devices do we own, where are they located, and what firmware version are they running?” If answering that question takes days, the organization may be carrying avoidable risk.
IoMT Visibility Should Include Firmware Versions
Internet of Medical Things, or IoMT, security programs often focus on device discovery and network behavior. Those are important, but firmware visibility should be part of the same process. Two identical devices may present different risk if they run different firmware versions.
Firmware version data helps security teams determine which assets require updates or compensating controls. It also allows organizations to prioritize devices affected by newly disclosed vulnerabilities. Without version visibility, vulnerability intelligence becomes much harder to turn into action.
Healthcare organizations should therefore connect device inventories with vulnerability-management processes. A firmware advisory should trigger a search across known devices, not a manual investigation from scratch. That integration shortens response time.
Procurement Decisions Shape Future Security
Firmware security can be difficult to add after purchase. Healthcare organizations evaluating connected devices should therefore ask cybersecurity questions during procurement rather than waiting until a vulnerability is discovered. Today’s buying decision determines tomorrow’s patching and incident-response options.
Important vendor questions include:
- Are firmware updates cryptographically signed?
- Does the device verify updates before installation?
- Can unauthorized firmware be prevented from executing?
- How are firmware vulnerabilities disclosed?
- How long will security updates be provided?
- What happens at end of support?
- Can firmware versions be inventoried remotely?
- What recovery mechanisms exist after corruption?
FDA’s current medical-device cybersecurity guidance emphasizes secure updateability and lifecycle vulnerability management. NIST also notes that firmware resiliency principles can support procurement strategies. Pasted markdown
End-of-Support Planning Is Part of Firmware Security
A medical device does not become safe simply because it continues functioning clinically. If firmware updates are no longer available, new vulnerabilities may accumulate without a direct remediation path. That creates long-term risk.
Healthcare organizations should know when firmware support ends and whether replacement or upgrade options exist. Devices approaching end of support should be included in capital planning before cybersecurity concerns become emergencies. Waiting until exploitation is active can dramatically narrow available options.
This planning should include clinical dependencies. Replacing a device may require interoperability testing, staff training, network changes, or workflow redesign. Early planning gives organizations more time to manage those transitions safely.
Network Segmentation Still Matters
Strong firmware protections do not eliminate the need for traditional cybersecurity controls. Connected medical devices should still be segmented according to their clinical and technical requirements. A compromised device should not automatically gain access to unrelated systems.
Healthcare organizations can restrict unnecessary communication, limit internet exposure, control vendor remote access, monitor unusual traffic, and maintain secure configurations around connected devices. HHS includes asset inventory, network segmentation, vulnerability mitigation, vendor risk management, and cybersecurity testing among its healthcare-specific performance goals. Pasted markdown
This creates defense in depth. Firmware integrity protects the low-level device, while network controls limit what happens if another layer fails. Security works best when no single control is expected to stop every attack.
Vendor Remote Access Deserves Additional Scrutiny
Medical device manufacturers may require remote access for maintenance or troubleshooting. That can be operationally necessary, but it creates another pathway into the environment. Healthcare organizations should limit remote access to the minimum required scope.
Vendor accounts should use strong authentication, defined support windows, and monitored sessions where feasible. Standing access should not remain active indefinitely if it is only required periodically. Access should also be removed when the vendor relationship or support need ends.
A vendor’s ability to update firmware gives it powerful access to the device. Healthcare organizations should understand how updates are distributed and whether vendor remote-access channels can affect low-level system configuration. Trust in the vendor should be supported by technical controls.
Monitor Devices That Cannot Monitor Themselves
Many medical devices do not support modern endpoint detection and response agents. Security teams may therefore need to rely more heavily on network telemetry and surrounding infrastructure. Understanding normal device behavior can make suspicious activity easier to identify.
Teams should know which systems a device normally communicates with, what protocols it uses, and when communication typically occurs. Unexpected connections or changes in network behavior may warrant investigation. Firmware-level compromise may not generate obvious operating-system alerts.
This is another reason segmentation and network monitoring are important. If endpoint visibility is limited, the environment around the device needs to provide additional evidence. The network can become part of the detection system.
Incident Response Should Include Firmware Escalation
Most cybersecurity playbooks are designed around applications, user accounts, endpoints, and operating systems. Medical device response procedures should also define when firmware needs to be considered. Not every incident requires firmware-level investigation, but the escalation path should exist.
Potential triggers may include:
- Unexpected firmware changes
- Boot-integrity failures
- Untrusted firmware updates
- Suspicious behavior persisting after an OS rebuild
- Vendor-confirmed firmware vulnerabilities
- Evidence suggesting pre-OS persistence
At that point, the manufacturer or specialized vendor may need to participate in the response. Actions could involve firmware validation, vendor-supported reprogramming, device isolation, or replacement depending on the evidence and the technology involved. Pasted markdown
Know When Reimaging Is Not Enough
Reimaging a compromised workstation is often a reasonable remediation step. The operating system is replaced, security controls are reinstalled, and the device can be validated before returning to service. This model works because the operating system is usually treated as the main trust boundary.
Firmware incidents challenge that assumption. If compromise occurs below the operating system, rebuilding the system above it may leave the malicious component untouched. Security teams therefore need criteria for deciding when ordinary remediation is no longer sufficient.
This is especially important for medical devices where aggressive troubleshooting can affect patient care or manufacturer support. Incident response should be carefully coordinated with clinical engineering and the device manufacturer. Cybersecurity remediation must preserve patient safety.
Protect, Detect, and Recover
NIST’s Protect, Detect, Recover model provides a useful framework for healthcare firmware security. Protection includes signed updates, secure boot, access restrictions, and strong device configuration. Detection includes verifying integrity, monitoring device behavior, and identifying unauthorized firmware changes.
Recovery is often the most overlooked component. Healthcare organizations should know how a device can return to a trusted firmware state if corruption occurs. That may require a known-good image, secure recovery partition, manufacturer support, or physical replacement.
A system without a trusted recovery path can become difficult to remediate after serious compromise. Procurement teams should therefore ask about recovery before devices enter production. The recovery process should not be discovered during an incident.
Final Thoughts
Medical device firmware security reminds healthcare organizations that cybersecurity does not stop at the operating system. Firmware controls fundamental device behavior, may execute before normal security software starts, and can create persistence challenges when compromised. Secure boot, signed updates, firmware inventory, network segmentation, lifecycle planning, vendor oversight, and recovery capabilities all contribute to reducing that risk.
The most important code on a medical device may be the code running before the operating system ever starts. Healthcare organizations should know how that code is protected, how updates are verified, and how trust can be restored if something goes wrong. For practical guidance on healthcare cybersecurity, medical device security, vulnerability management, HIPAA risk management, penetration testing, and cyber resilience, follow Tempest Healthcare IT on LinkedIn: https://www.linkedin.com/company/tempesthealthcareit/