Healthcare Voice Security: Protecting Patients, Care Teams, and Critical Communications in 2026
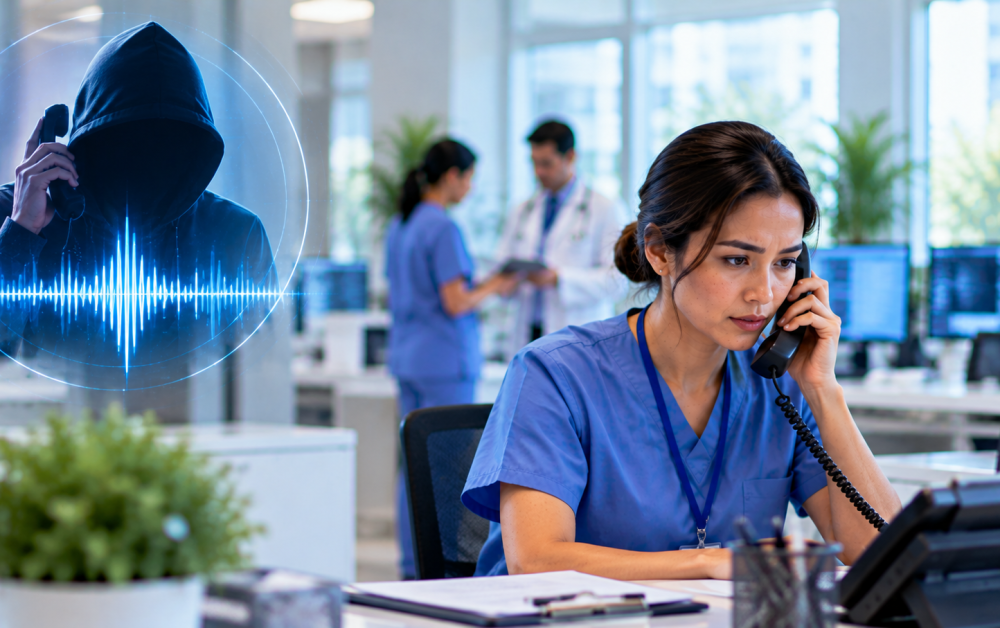
Imagine a receptionist receiving an urgent telephone call from someone claiming to represent the practice’s electronic health record (EHR) provider. The caller knows the software vendor’s name, speaks confidently, and insists that an immediate repair requires installing a remote support application. Although the request sounds legitimate, approving it without verification could expose sensitive systems to unauthorized access.
This hypothetical scenario illustrates why healthcare voice security deserves greater attention from U.S. healthcare organizations. Cybercriminals can exploit telephone conversations to manipulate employees, obtain sensitive information, or persuade staff to perform unauthorized actions. For small and medium-sized medical practices, these attacks can threaten patient privacy, operational continuity, and trust.
On October 20, 2026, the American Hospital Association (AHA) scheduled a sponsored webinar titled Voice Security: Protecting Patients, Care Teams & Critical Communications, featuring experts from Mutare. The announced discussion addresses voice-based threats, healthcare operational risks, and layered protection strategies. Its themes highlight an important cybersecurity principle: protecting healthcare communications requires both technical safeguards and reliable employee verification procedures.
What Is Healthcare Voice Security?
Healthcare voice security refers to the practices and technologies used to protect telephone communications, voice systems, and call-related workflows against fraud, impersonation, unauthorized access, and disruption. It includes traditional telephone services, Voice over Internet Protocol (VoIP) systems, call-routing platforms, voicemail, and interactions between employees and external callers. Effective protection also requires employees to recognize when a seemingly routine conversation involves an unusual or unauthorized request.
Unlike email security, voice security involves decisions made during live conversations. Attackers may use urgency, authority, familiarity, or emotional pressure to influence employees before they can verify a request. A convincing telephone interaction can become the starting point for a broader cybersecurity incident.
Healthcare organizations should therefore treat voice communications as part of their overall digital attack surface. Telephone workflows often connect directly to identity verification, account recovery, patient information, and remote technical support. These connections make voice security relevant to both cybersecurity risk management and daily clinical operations.
Understanding Vishing and Voice-Based Cyberattacks
Vishing, or voice phishing, is a form of social engineering conducted through telephone or other voice communications. Attackers attempt to persuade individuals to disclose confidential information, approve access, transfer money, or perform actions that compromise security. The attack depends primarily on manipulating human decisions rather than directly exploiting a software vulnerability.
Healthcare practices encounter many legitimate callers throughout the day, including patients, pharmacies, laboratories, insurance companies, and technology vendors. Attackers can imitate these interactions to make fraudulent requests appear routine. A receptionist or billing employee may have limited time to distinguish an authorized request from a carefully prepared impersonation attempt.
Voice-based threats can involve several techniques:
- Vishing: Fraudulent calls designed to obtain information or influence employee behavior.
- Caller ID spoofing: Manipulating displayed caller information to impersonate a trusted number.
- AI voice impersonation: Using synthetic or manipulated audio to imitate a person’s voice.
- Technical support impersonation: Pretending to represent an IT department or software provider.
- Payment diversion: Requesting unauthorized changes to banking or vendor payment details.
- Robocall abuse: Using automated calling systems to overwhelm or manipulate communications.
These methods can be combined with information obtained from public websites, social media, or previous communications. Attackers may know employee names, vendor relationships, or commonly used software products. Familiar details should not be treated as proof that a caller is authorized.
Why Voice Security Matters for U.S. Healthcare Practices
Healthcare organizations depend on reliable telephone communications to coordinate patient care and manage essential business functions. Calls support appointment scheduling, referrals, prescription questions, insurance verification, laboratory coordination, and urgent clinical communication. Disruptions or fraudulent instructions can therefore affect multiple departments.
For smaller healthcare practices, telephone workflows may be handled by employees with several simultaneous responsibilities. Receptionists, billing specialists, practice managers, and clinical personnel often make decisions while responding to patients and managing administrative tasks. Attackers may exploit these conditions by creating a false sense of urgency.
Voice-based cyberattacks can also create consequences beyond the telephone system itself. A successful impersonation attempt might lead to unauthorized remote access, compromised credentials, fraudulent payments, or inappropriate disclosure of patient information. Healthcare voice security should therefore be integrated with identity protection, access management, and incident-response planning.
1. Establish Independent Caller Verification Procedures
One of the most effective ways to reduce voice-based social engineering risk is to establish clear verification procedures. Employees should know which requests require additional confirmation before any action is taken. These procedures should apply consistently, regardless of how confident or familiar a caller sounds.
Requests involving sensitive information, payment changes, account resets, or remote technical support should receive particular attention. Staff should verify the caller’s authority using established organizational records or previously approved contact information. A callback number supplied during a suspicious conversation should not be considered independent verification.
Healthcare organizations should also provide employees with a simple response when verification is necessary. A practical example is: “I need to verify this request through our established process before proceeding.” Leadership should support employees who follow this procedure, even when a caller insists that the matter is urgent.
2. Protect Remote Support and Vendor Access
Healthcare practices frequently rely on external technology providers to maintain EHR platforms, scheduling applications, network infrastructure, and connected equipment. Remote support can be essential for resolving technical problems efficiently. However, unauthorized support sessions may expose systems to malicious software or inappropriate administrative access.
An unexpected telephone call should never be sufficient authorization to install a remote-access application. Healthcare IT teams should establish approved support tools, authorized vendor contacts, and documented procedures for initiating sessions. Employees should know how to distinguish scheduled maintenance from unsolicited technical requests.
Remote-access permissions should also be restricted to legitimate operational requirements. Administrative sessions should use appropriate authentication, access controls, and logging. These safeguards can help reduce the impact of a successful impersonation attempt.
3. Secure Account Recovery and Help Desk Verification
Attackers may attempt to exploit account recovery procedures by impersonating employees, administrators, or vendors. A caller might claim to have lost access to an authentication device or urgently need a password reset. If support personnel rely on familiarity or urgency instead of verification, the recovery process can become a security weakness.
Healthcare organizations should define identity verification requirements for password resets, MFA enrollment changes, and privileged account recovery. These procedures should use approved verification methods rather than information easily obtained from public sources. Exceptions should require appropriate authorization and documentation.
CISA recommends multifactor authentication for remote access and privileged accounts. However, MFA protections can be weakened when account recovery procedures allow attackers to bypass them through social engineering. Secure enrollment, recovery, and administrative oversight are therefore essential parts of healthcare identity security.
4. Review Healthcare Phone System Security
Telephone infrastructure requires security management just like other business technology. Modern healthcare phone systems may include cloud-based administration, call forwarding, voicemail, automated attendants, and integrations with business applications. Unauthorized changes to these features can affect communication availability or redirect sensitive calls.
Healthcare IT teams should review who can modify phone routing, voicemail settings, provider accounts, and administrative configurations. Unnecessary permissions should be removed, and important administrative accounts should receive appropriate authentication protection. Providers should also explain available fraud alerts, monitoring features, and account recovery procedures.
Call filtering may help reduce unwanted traffic, but healthcare organizations must consider the possibility of blocking legitimate communications. Patients, caregivers, laboratories, and referral partners may call from unfamiliar numbers. Changes should be tested carefully to preserve access to essential services.
5. Recognize AI Voice Impersonation and Deepfake Risks
Artificial intelligence has introduced additional concerns surrounding voice-based social engineering. AI-generated or manipulated audio may imitate a familiar person’s speech patterns, potentially making fraudulent requests more convincing. Healthcare employees should understand that a recognizable voice is not sufficient evidence of identity.
An attacker could theoretically impersonate a practice administrator, vendor representative, or other trusted contact to request a sensitive action. The risk becomes more significant when the requested action involves financial transfers, account changes, patient information, or privileged access. Verification procedures should address the request itself rather than relying on an employee’s ability to identify synthetic audio.
Healthcare cybersecurity awareness training should avoid presenting deepfake detection as the primary defense. Employees may not be able to reliably distinguish authentic speech from manipulated audio during a live conversation. Independent verification and clearly defined authorization procedures provide a more dependable approach.
6. Train Employees Using Healthcare-Specific Scenarios
Healthcare cybersecurity awareness training should reflect the telephone interactions employees encounter during normal operations. Generic examples may explain social engineering concepts, but realistic scenarios help staff understand when additional verification is necessary. Training should be short, practical, and relevant to each department.
Useful healthcare voice security scenarios include:
- A caller impersonating an EHR technician requesting remote access.
- A vendor representative asking to change payment information.
- An individual requesting patient records without adequate authorization.
- A caller claiming to be a practice administrator requesting an urgent account reset.
- A supposed IT employee asking someone to approve an unexpected MFA notification.
After each scenario, employees should discuss what information requires verification and which department should handle the request. Training should also explain how to report a suspicious interaction and what to do if access was already granted. The objective is to improve decision-making rather than test whether employees can identify every possible scam.
Healthcare organizations should encourage early reporting without creating a culture of blame. Employees who disclose suspicious calls or possible mistakes provide valuable information for investigation. Prompt reporting may help security teams contain unauthorized activity before additional systems are affected.
7. Monitor Suspicious Voice and Account Activity
Technical monitoring can complement employee verification procedures by identifying unusual activity across communication systems and connected accounts. Healthcare organizations should ask their telecommunications providers about available alerts for abnormal calling patterns, administrative changes, and potential fraud. These capabilities vary by provider and should be evaluated against operational requirements.
Security teams should also consider what happens after a suspicious call. If an employee approves remote access or discloses credentials, relevant endpoint, identity, and application activity may require investigation. Reviewing associated logs can help determine whether unauthorized actions occurred.
Monitoring responsibilities should be clearly assigned. An alert provides limited protection if nobody is responsible for reviewing it or initiating a response. Healthcare IT teams should establish escalation procedures that connect telecommunications concerns with broader cybersecurity operations.
8. Prepare for Disrupted Patient Communications
Healthcare voice security also involves maintaining communication availability during disruptions. Telephone outages, unusual call traffic, or compromised routing systems may affect appointments, referrals, patient inquiries, and coordination with external providers. Business continuity planning should account for these dependencies.
Healthcare organizations should identify approved alternative communication methods and establish procedures for activating them. Emergency contacts, escalation responsibilities, and patient communication requirements should be documented in advance. Alternative channels must also be evaluated for privacy and security considerations.
A short tabletop exercise can help practices test their preparedness. Clinical and administrative staff should discuss how essential communications would continue if the primary telephone system became unavailable. Findings should be documented with assigned owners and completion dates.
How Healthcare Voice Security Supports HIPAA Readiness
Voice security contributes to broader efforts to protect patient information and maintain appropriate access controls. Although HIPAA does not establish a universal requirement for a particular telephone security product, regulated organizations must implement applicable safeguards protecting electronic protected health information. Voice-related workflows should be considered when they create risks involving ePHI or connected information systems.
For example, a fraudulent support call may result in unauthorized access to an application containing sensitive information. Similarly, improper account recovery could allow an attacker to access systems used for patient communications or administration. These scenarios demonstrate why telephone-based threats should be considered within broader security risk assessments.
Healthcare organizations should document relevant verification procedures, access controls, employee training, and incident-response responsibilities. These records help establish consistency and support ongoing risk management. Security measures should reflect actual workflows rather than relying exclusively on written policies.
A Practical Healthcare Voice Security Checklist for Q4 2026
Healthcare practices can begin strengthening voice security without introducing an entirely new technology program. The first priority should be identifying telephone interactions that could lead to sensitive disclosures, account changes, financial transactions, or system access. These workflows should receive clear verification and authorization requirements.
A practical review should address:
- Independent verification of sensitive telephone requests
- Approved remote-support procedures
- Help desk identity verification
- MFA enrollment and recovery safeguards
- Phone system administrative permissions
- Vendor and telecommunications provider contacts
- Employee reporting procedures
- Suspicious call and account activity monitoring
- Communication outage and recovery planning
After identifying gaps, healthcare leaders should assign responsibility for corrective actions. Improvements should be tested through realistic scenarios and reviewed with the employees who use the procedures. The goal is to make secure decisions easier during everyday operations.
Final Thoughts
Healthcare voice security is an increasingly important part of protecting patients, care teams, and critical communications. Vishing, caller ID spoofing, AI voice impersonation, and fraudulent technical support requests demonstrate how telephone conversations can become pathways to broader cybersecurity incidents. Healthcare organizations should combine independent verification, secure access controls, employee awareness, technical monitoring, and communication continuity planning.
Small and medium-sized healthcare practices can strengthen their defenses by making verification procedures consistent and easy to follow. Protecting sensitive information requires recognizing that a convincing caller is not necessarily an authorized caller. For more insights on healthcare cybersecurity, voice phishing prevention, AI impersonation, HIPAA readiness, vulnerability management, penetration testing, and patient data protection, follow Tempest Healthcare IT on LinkedIn.