ACO Cybersecurity: How Cyber Risk Profiling Protects Connected Care
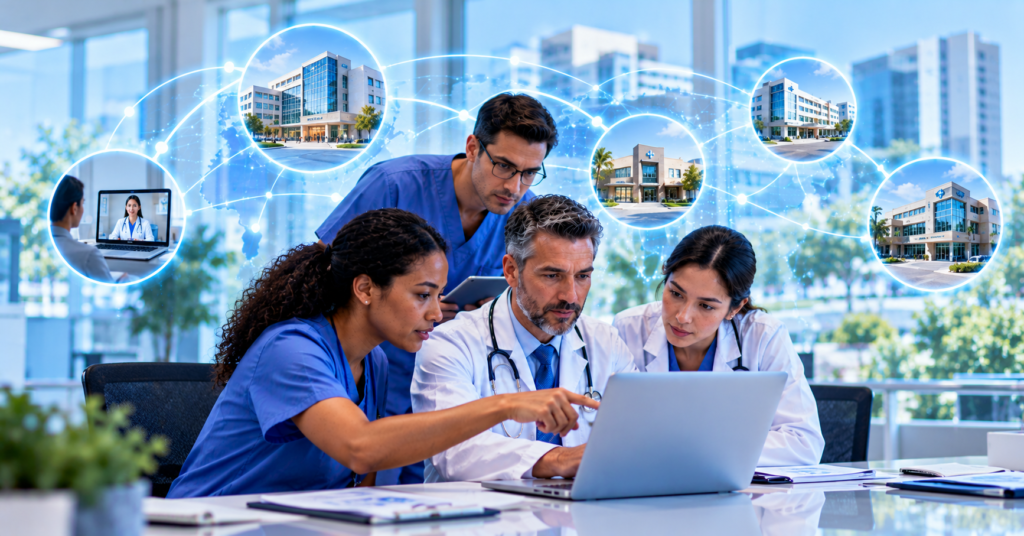
A hospital may operate a mature cybersecurity program while an affiliated physician practice struggles with outdated software, weak authentication, and limited IT resources. When these organizations exchange patient information or access shared clinical applications, their security decisions can affect the broader healthcare network. This interconnected environment makes ACO cybersecurity an increasingly important consideration for healthcare leaders in 2026.
Accountable Care Organizations (ACOs) bring healthcare providers together to coordinate patient care, improve outcomes, and manage healthcare costs. According to the Centers for Medicare & Medicaid Services (CMS), ACOs may include physicians, hospitals, and other healthcare professionals working toward shared quality and financial objectives. Their collaboration often depends on digital systems that connect otherwise independent organizations.
However, participation in an ACO does not automatically create unrestricted access between members. Cybersecurity risks arise from the specific connections, permissions, and shared services supporting coordinated care. ACO cyber risk profiling helps organizations identify these exposures, evaluate their consequences, and prioritize improvements that protect patient information and clinical operations.
What Is ACO Cyber Risk Profiling?
ACO cyber risk profiling is a structured process for evaluating cybersecurity exposure across participating healthcare organizations and their shared digital environment. It examines security controls, user identities, technology integrations, vendor relationships, and operational dependencies. The objective is to understand how a weakness within one organization could affect connected healthcare services.
Unlike a traditional assessment focused on a single facility, ACO risk profiling considers relationships between multiple organizations. A small medical practice may connect to a shared EHR, population health platform, referral network, or analytics service. These connections create security responsibilities that extend beyond the practice’s internal network.
An effective risk profile should identify the affected systems, potential consequences, and organizations responsible for remediation. It should also distinguish confirmed vulnerabilities from assumptions about risk. Evidence-based findings provide a stronger foundation for cybersecurity planning than questionnaire scores alone.
Why Cybersecurity Matters for Accountable Care Organizations
ACOs depend on collaboration between healthcare providers that may have different budgets, technologies, and security capabilities. Large hospitals may maintain dedicated security teams, while smaller practices often rely on external IT providers or limited internal resources. These differences can make consistent cybersecurity oversight challenging.
Connected care also increases the importance of protecting information exchanged across organizational boundaries. Shared patient records, clinical referrals, population health analytics, and care coordination platforms may contain sensitive information. Unauthorized access or service disruption can affect multiple participants depending on how these systems are configured.
Cybersecurity incidents may also interfere with the operational goals of coordinated care. An unavailable shared platform could delay referrals, disrupt communication, or limit access to information needed for treatment decisions. ACO cybersecurity planning should therefore address both patient data protection and healthcare service continuity.
1. Understand That ACO Membership Does Not Automatically Create an Attack Path
The phrase “an ACO is only as strong as its weakest link” highlights the importance of shared security responsibilities. However, it can oversimplify how cybersecurity threats move between healthcare organizations. Membership alone does not mean that one practice has unrestricted access to every participating hospital or clinical system.
A cybersecurity incident can affect connected organizations when an exploitable pathway exists. Examples include excessive application permissions, shared credentials, insecure remote access, or inadequately protected integrations. The potential impact depends on what the compromised account or system can actually reach.
Consider a hypothetical physician practice whose employee credentials are compromised through phishing. If the account can access extensive population health datasets, the potential exposure may extend beyond the practice’s immediate operations. If permissions are restricted to a narrow clinical workflow, the consequences may be more limited.
ACO cyber risk profiling should evaluate actual access and system dependencies rather than assuming every participant creates the same risk. This distinction helps healthcare leaders prioritize meaningful vulnerabilities. It also supports more accurate communication about shared cybersecurity exposure.
2. Map Shared Healthcare Systems and Data Connections
The first practical step in ACO cybersecurity risk profiling is identifying the systems connecting participating organizations. These may include shared EHR platforms, health information exchanges, referral systems, analytics applications, and secure file-transfer services. External vendors supporting these platforms should also be included.
Healthcare IT teams should document the purpose of each connection and the information exchanged. They should identify which organizations, employees, applications, and automated accounts can access the service. This information helps establish where cybersecurity responsibilities begin and end.
Identify Direct and Indirect Dependencies
Not every shared cybersecurity risk involves direct access between healthcare networks. Several ACO participants may rely on the same cloud provider, billing company, or population health platform. An outage affecting that provider could disrupt coordinated care even without compromising the internal systems of participating organizations.
Risk assessments should therefore examine service availability alongside unauthorized access and data exposure. Healthcare organizations need to understand which external systems are essential for clinical and administrative workflows. Mapping these dependencies supports more effective incident response and recovery planning.
3. Establish a Common ACO Cybersecurity Baseline
Participating healthcare organizations do not need identical technology to establish consistent security expectations. A shared cybersecurity baseline can define minimum outcomes while allowing each participant to use controls appropriate to its environment. This approach is particularly useful when organizations differ significantly in size and technical resources.
The U.S. Department of Health and Human Services provides voluntary Healthcare and Public Health Cybersecurity Performance Goals that can inform security prioritization. These goals address important areas such as multifactor authentication, vulnerability mitigation, email security, incident preparedness, and network segmentation. ACO leaders can use relevant goals as a reference when developing shared security expectations.
Translate Security Goals Into Verifiable Evidence
A cybersecurity baseline should include questions that organizations can answer with supporting evidence. For example, participants may document MFA coverage for shared applications, access-removal procedures, vulnerability management practices, and incident-response responsibilities. These records provide more useful information than a simple statement that security policies exist.
Exceptions should also be documented with a clear business justification and responsible owner. Smaller practices may require phased improvements or technical assistance to meet agreed expectations. The objective is measurable risk reduction rather than uniform technology adoption.
4. Prioritize Cyber Risk Based on Exposure and Consequence
Not every cybersecurity weakness creates the same level of risk for an ACO. Prioritization should consider the sensitivity of accessible information, system permissions, known vulnerabilities, and importance of the affected clinical workflow. Detection capabilities, containment options, and recovery readiness should also influence decisions.
A small practice with limited access and verified safeguards may create less shared exposure than a larger organization with excessive privileges. Similarly, a third-party integration with broad permissions may deserve significant attention regardless of the vendor’s size. Risk should be evaluated according to technical evidence and operational consequences.
Avoid Overreliance on Numerical Risk Scores
Cybersecurity scoring systems can help organize findings, but a numerical rating is not a precise prediction of a future incident. Assessors should explain the evidence supporting each risk classification and acknowledge relevant uncertainty. Healthcare leaders need to understand what could happen and why a particular weakness deserves attention.
Each significant finding should lead to an actionable remediation plan. The plan should identify the responsible organization, required improvement, target date, and verification method. This approach turns cybersecurity assessments into measurable operational decisions.
5. Strengthen Identity and Access Management Across ACO Participants
Identity and access management is a critical component of ACO cybersecurity because participating organizations may share applications without sharing internal networks. Clinicians, administrators, vendors, and automated integrations can require different levels of access. Poorly managed permissions may increase the impact of compromised accounts.
Healthcare organizations should apply least-privilege principles wherever supported. Employees should receive access appropriate to their responsibilities, while administrative privileges should remain restricted. Access reviews should account for role changes, employee departures, and changes in ACO participation.
Protect Privileged and Automated Accounts
Automated service accounts and application integrations can present risks when permissions remain broader than necessary. These accounts may operate continuously without a person signing in each day. Healthcare IT teams should assign ownership and periodically review their access.
Privileged accounts should receive additional safeguards, including appropriate authentication and monitoring. Authorized security validation can help determine whether access boundaries operate as intended. Testing should be coordinated with system owners to protect clinical availability.
Final Thoughts
ACO cybersecurity in 2026 requires healthcare leaders to understand how independent organizations interact through shared systems, identities, vendors, and clinical workflows. Cyber risk profiling provides a structured way to identify where vulnerabilities could affect more than one participant. Effective assessments should focus on actual technical exposure, operational dependencies, and evidence-based remediation priorities.
A strong ACO cybersecurity program combines common security expectations with appropriate flexibility for participating organizations. Clear access controls, coordinated incident response, vendor oversight, and continuous risk review can help protect connected healthcare services. For more insights on ACO cybersecurity, healthcare cyber risk profiling, HIPAA readiness, vulnerability assessments, penetration testing, third-party risk management, and healthcare cyber resilience, follow Tempest Healthcare IT on LinkedIn.